Wireless is essential to modern workplaces. It gives staff mobility, supports devices that have no practical Ethernet connection and makes it easier to adapt spaces without running a new cable for every change. But that flexibility does not make Wi-Fi a substitute for structured cabling.
A reliable network is built from complementary technologies. Wireless provides convenient access; structured cabling provides a predictable physical foundation for access points, switches, servers, workstations and operational technology. Treating one as a replacement for the other can create reliability problems and security blind spots that are difficult to diagnose—especially at 2am, when a “temporary” workaround becomes a business outage.
The distinction matters for more than performance. Physical infrastructure is part of cybersecurity. Cabling, patch panels, switches and access points determine where traffic can travel, how devices are separated, and whether monitoring tools can see what is https://smoothdecorator.com/what-is-the-quickest-win-for-network-security-without-new-software/ happening. A well-designed wireless network still depends on a well-designed wired one.
Wireless and cabling solve different problems
Wi-Fi is a shared radio service. Devices contend for airtime, and the quality of a connection can change with distance, building materials, neighbouring networks and the number of active clients. This makes wireless valuable for mobility, but less predictable than a dedicated, correctly installed Ethernet connection.
Structured cabling is the organised physical system of cable runs, outlets, patch panels and connections to network switches. When it is properly designed, installed, tested and labelled, it provides stable links between devices and the network. That wired reliability is particularly important for fixed equipment, infrastructure and services where interruption has a tangible cost.
Requirement Wireless is well suited to Structured cabling is well suited to Mobility Laptops, phones and roaming users Fixed endpoints and network equipment Predictable connection Best-effort access where movement matters Stable links for critical or stationary devices Network expansion Adding supported wireless clients Connecting access points, switches and fixed devices Security design Authentication, encryption and radio coverage controls Physical connectivity, switching and segmentationThe practical goal is not “wired versus wireless”. It is choosing the right connection for each use case, while making sure the underlying network can support both.
Wireless interference is a real operational constraint
Radio spectrum is shared. Nearby access points, neighbouring businesses, consumer devices, building materials and even poorly chosen channel plans can affect wireless performance. The result may be slow connections, dropped sessions or inconsistent coverage—without an obvious broken cable or failed port to point to.
That is the nature of wireless interference: it can vary by location and time. A meeting room may work well in the morning and become unreliable when the office is full. A new fit-out or a change in furniture can alter radio conditions. A device may appear connected while struggling to communicate effectively.
Wireless surveys, careful access-point placement and sensible radio configuration are important. So are capacity planning and ongoing monitoring. But these measures do not remove the fundamental trade-off: Wi-Fi uses shared media, and performance depends on radio conditions beyond the organisation’s complete control.
For fixed equipment, a cable often avoids those uncertainties. A desktop, printer, camera, access point or industrial controller that does not need to move may be better served by Ethernet. That does not mean every endpoint must be wired; it means not using wireless by default where a dependable physical connection is practical and appropriate.
Physical faults can cause outages and security blind spots
Physical infrastructure is sometimes treated as “just plumbing”. That is a mistake. A damaged cable, loose connector, overloaded switch, unlabelled patch panel or undocumented connection can interrupt service. It can also make it harder to understand which device is connected where, what network it belongs to, and whether its traffic is being monitored.
When physical-layer problems are difficult to diagnose, teams may work around them by moving devices, adding an unmanaged switch or connecting equipment wherever a spare port is available. Those quick fixes can create an undocumented path between network segments. The result is not only a reliability issue; it may also be a security control failure.
Think of a patch panel with ports that have not been labelled, or a switch tucked behind a cabinet with unknown connections. During an incident, investigators need to establish which systems communicated, through what path, and whether a connection bypassed expected controls. Mystery cables turn that job into guesswork.
Good physical practice reduces both operational risk and security uncertainty:
- Label outlets, patch panels, switch ports and cable runs consistently. Document what is connected, where it is connected and why. Test and certify cabling rather than relying on appearance. Keep network cabinets secure, tidy and appropriately cooled. Remove or disable unused connections in accordance with policy. Control the use of unmanaged switches in production environments.
These are not cosmetic details. They help teams maintain service, investigate faults and verify that the intended network design is the one actually in use.
Segmentation depends on capable switching and correct design
Security segmentation is often discussed as if it were a software setting. In practice, it depends on capable network equipment, a clear design and correct configuration. Managed switches, VLANs, routing controls, access policies and monitoring all have roles to play. If the switching layer cannot enforce the design, or if connections are patched incorrectly, segmentation on a diagram may not match segmentation on the floor.
A flat network puts too much reliance on endpoint security and perimeter controls. When everything shares one broadcast domain, a compromised or misconfigured device may have more opportunity to discover and communicate with other systems. Separating user devices, servers, guest access and operational technology can reduce unnecessary reachability and limit the impact of an incident.
Segmentation is not achieved simply by buying a switch that supports VLANs. The organisation needs to define which devices should communicate, where traffic should be routed, and how those flows will be controlled and observed. Switch configuration, port assignment, wireless network mapping and firewall policy must agree.
Companies such as Cisco provide switching and wireless platforms that can support these designs. The specific product matters less than selecting equipment that fits the operational requirements, managing it properly and configuring it to match the security architecture. A capable managed switch is not a substitute for sound design—and a sophisticated firewall cannot compensate for a physical network that silently bypasses it.
Wireless still relies on the wired network
In most business environments, wireless access points connect back to Ethernet switching. Their traffic then traverses the wired network to reach services, security controls and the internet. If the cable to an access point is faulty, its switch is misconfigured, or the uplink is saturated, the wireless service may fail even when the radio itself is working normally.
That dependency Click to find out more is easy to overlook. Replacing user connections with Wi-Fi does not remove the need for switching, uplinks, patching and structured cable runs. It often increases the importance of those components because access points need reliable power and network connectivity across the building.
Critical environments need deliberate connection choices
In offices, a wireless-first approach can make sense for staff laptops and mobile devices. In warehouses, healthcare settings, manufacturing sites and other operational environments, the decision needs more care. Some endpoints move; others are fixed, safety-relevant or sensitive to interruption. A network serving industrial equipment may have different availability, environmental and support requirements from one serving meeting-room laptops.
Industrial networking suppliers such as MOXA offer equipment designed for demanding operational environments. Choosing suitable equipment is only one part of the job: topology, power, environmental conditions, access control, monitoring and maintenance arrangements also matter. A wireless link should be used where its mobility benefits justify its operational characteristics, not simply because running cable seems inconvenient.
Structured cabling also supports the wireless network itself. Access points placed in the right locations need suitable cable paths, appropriate switching and often Power over Ethernet. Planning this as part of a fit-out is generally more robust than relying on ad hoc placement and improvised cabling after staff report dead spots.
Security tools depend on trustworthy network foundations
Firewalls and endpoint detection platforms are important security controls, but they do not make the physical network irrelevant. Firewalls can control traffic at defined boundaries. Endpoint detection platforms can help identify suspicious activity on supported devices. Both are more useful when the network’s topology, device inventory and traffic paths are understood.
When devices are connected through undocumented switches or patched to unexpected ports, it becomes harder to confirm which controls apply. Monitoring coverage may be incomplete, network policies may be inconsistent, and incident responders may waste time establishing basic facts.
Wireless needs its own controls too: strong authentication, appropriate encryption, separation of guest and corporate access, careful management of access points, and review of rogue or unauthorised equipment. These controls complement—not replace—wired security. A secure wireless network still needs a trusted switching and routing design behind it.
What ACSC guidance assumes
Australian Cyber Security Centre (ACSC) guidance addresses cyber risk through practical controls, including managing access, protecting systems and maintaining visibility. These controls depend on an organisation knowing what is connected and being able to enforce its policies consistently. That is much harder when the underlying network is undocumented, unmanaged or physically inconsistent.

ACSC guidance is not a cabling specification. However, applying security guidance effectively assumes solid network foundations: reliable equipment, defined boundaries, controlled connections and enough documentation to understand the environment. A security policy that says “separate these systems” is not effective if the physical switching and patching do not implement that separation.
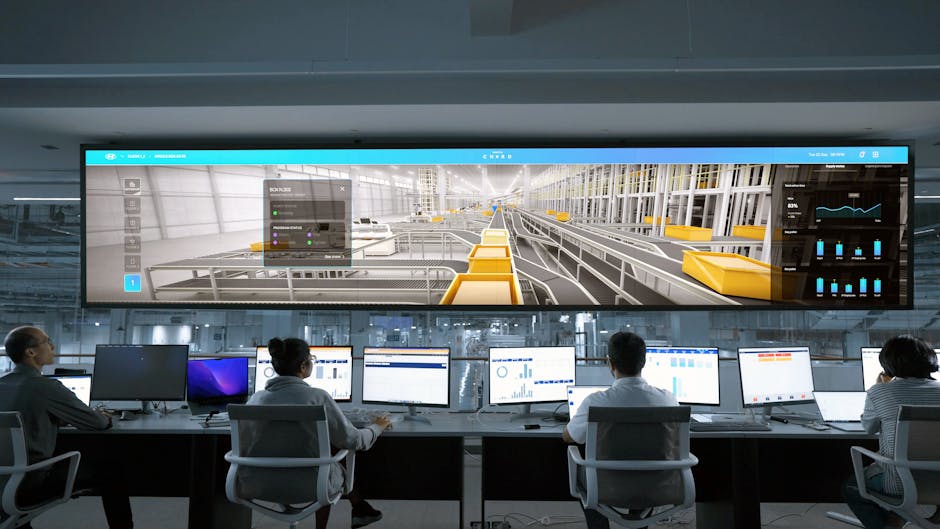
For network teams, the takeaway is straightforward: physical infrastructure belongs in security planning, procurement, change control and incident response. It is not a separate facilities concern to be addressed only when someone loses connectivity.
A practical design approach
Before deciding that wireless can replace cabling, ask what each device needs and what happens when its connection fails. A useful design process includes:
Classify the endpoints. Identify which devices are mobile, fixed, business-critical, operational or guest-facing. Set connection requirements. Consider availability, throughput, latency, roaming, environmental conditions and supportability. Design the wired foundation. Plan cable paths, patch panels, managed switches, uplinks, power and capacity for both endpoints and access points. Define segmentation. Map device groups to network segments and specify which communications are required and allowed. Validate the wireless layer. Survey coverage and capacity, account for interference, and test in realistic operating conditions. Document and test. Label connections, maintain diagrams, verify configurations and rehearse recovery from common failures.Ask the operational question as well: what happens at 2am when this fails? Can the on-call team identify the affected cable, switch port, access point and network segment? Is there a tested fallback? Can they restore service without introducing an unmanaged device or an undocumented connection?
Use both technologies for what they do best
Wireless is an excellent way to give people and devices mobility. Structured cabling is the dependable physical foundation that connects fixed systems, supports access points and enables a manageable network. The strongest designs use each where it fits, rather than treating one as a universal replacement for the other.
When planning a network, include cabling and switching in cybersecurity decisions from the start. Build for wired reliability where predictability matters, manage wireless interference and shared media where mobility is needed, and make segmentation real through capable equipment and careful configuration. Label the ports, document the paths and remove the mystery from the cabinets.
Good infrastructure is not glamorous, but it is what lets security controls work as intended—and what helps keep a routine fault from becoming an outage, a blind spot or an incident.